Software Supply Chain Security
What are we doing?
In an era where software systems underpin critical infrastructure, ensuring their security and reliability is paramount. However, the evolving complexity of modern software poses significant challenges for traditional security measures. Our project is dedicated to fortifying software security and reliability through a multifaceted approach that integrates cutting-edge techniques and methodologies. We focus on leveraging advanced technologies such as Large Language Models (LLMs) and Static Program Analysis to safeguard individual program and software supply chains against a wide range of security threats. Ultimately, our goal is to empower organizations to proactively identify, mitigate, and prevent security threats, thereby safeguarding critical infrastructure, sensitive data, and user privacy.
Recent Updates
- Sep, 2025 Our ICSME'25 papers "Code Property Graph Meets Typestate: A Scalable Framework to Behavioral Bug Detection" won IEEE TCSE Distinguished Paper Award.
- Mar, 2024 Our papers "API Misuse Detection via Probabilistic Graphical Model" and "Model-less Is The Best Model: Generating Pure Code Implementations to Replace On-device DL Models" have been accepted by ISSTA 2024 research paper track.
- Mar, 2024 Our SANER'24 paper "Investigating and Detecting Silent Bugs in PyTorch Programs" won IEEE TCSE Distinguished Paper Award.
- Jan, 2024 our paper "ProveNFix: Temporal Property guided Program Repair" has been accepted by the FSE'24 research papers track.
- Aug, 2023 our paper "Automated Fixing of Web UI Tests via Iterative Element Matching" has been accepted by the ASE'23 research papers track.
- Dec, 2022 our paper "Template-based Neural Program Repair" has been accepted by the ICSE'23 technical track.
- Dec, 2022 our paper "A Collaboration-Aware Approach to Profiling Developer Expertise with Cross-Community Data" has been accepted by the QRS'22 regular papers track.
- Jul, 2022 Wang Jing has successfully defended her master thesis, and won Outstanding Graduates award of Beihang University. She is moving to Bank of China.
- Jun, 2022 Yongqiang's work on developer portrait has beed accepted by Huawei OpenEuler Community.
- Apr, 2022 our paper "Program Vulnerability Repair via Inductive Inference" has been accepted by the ISSTA'22 technical papers track.
Current Projects
Software Supply Chain security
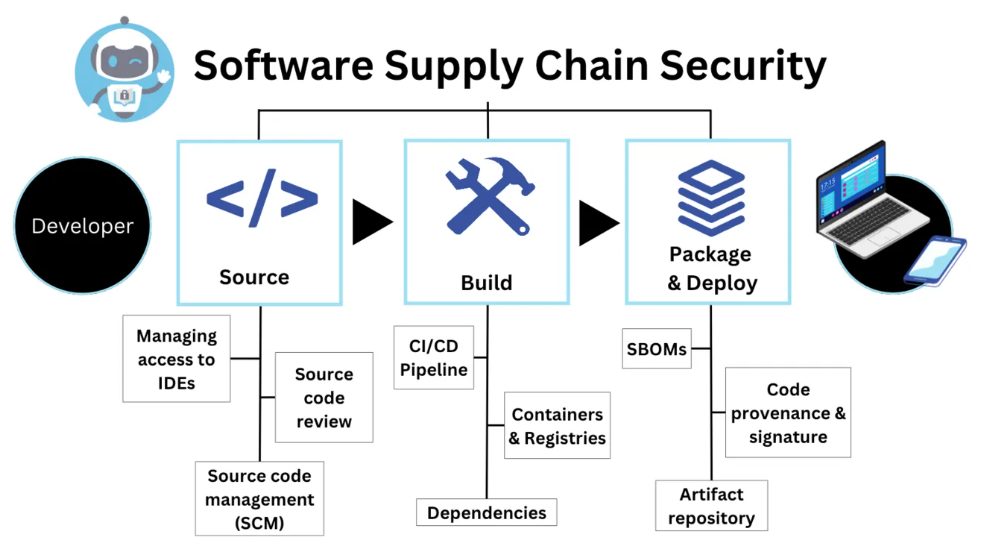
Software supply chains play a critical role in delivering reliable and secure software products to end-users. However, recent high-profile security breaches and supply chain attacks have highlighted the vulnerabilities inherent in these systems. This project focuses on enhancing software supply chain security through innovative techniques such as fine-grained program dependency construction, clone detection, vulnerability recognition, vulnerability propagation analysis, security pre-warning, and more. The ultimate goal of this project aligns closely with the principles of AppSecOps, aiming to integrate security practices into the application development and operations processes to enhance the security of software applications throughout their lifecycle. We aim to help organizations build and deploy more secure, resilient, and reliable software applications in today's rapidly evolving threat landscape.
LLM for software security analysis
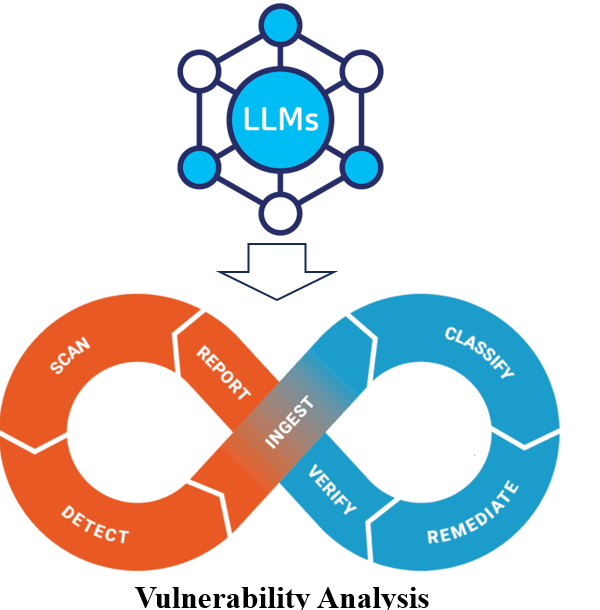
In response to security and reliability issue in individual programs and software supply chain, this project harnesses the power of Large Language Models (LLMs) to revolutionize software security practices. This project aims to develop an advanced software security solution that leverages LLMs to automate and enhance test case generation, vulnerability detection, localization, and repair processes. By harnessing the immense language understanding capabilities of LLMs, we seek to significantly improve the efficiency, accuracy, and scalability of software security practices.
Static program analysis based on CPG [Link]
In addition to leveraging LLMs, we are advancing vulnerability detection through static program analysis. Our project focuses on developing a novel Simplified Code Property Graph (S-CPG), which optimizes away unnecessary nodes and edges compared to the original (Joern) while preserving essential semantic information. Currently, we have implemented S-CPG for C, Java, Python, and ArkTS. We also provide a user-friendly Domain Specific Language (DSL) that enables users to define query patterns on S-CPG intuitively and efficiently, without requiring in-depth knowledge of the underlying graph structure. To date, we have identified over 30 issues in open-source projects, with more than 20 confirmed by project developers. Below are some CVE-ids discovered by our S-CPG: CVE-2024-48210, CVE-2025-25623, CVE-2025-29498, CVE-2025-29499, CVE-2025-29502, CVE-2025-4001, CVE-2025-4002, CVE-2025-4003
Publications
Selected Research Papers
-
SLIT: Execution-Grounded Small Language Models for Issue-Reproducing Test Generation
Runlin Liu, Zhe Zhang, Zeren Chen, Xiang Gao, Lu Sheng, Ping yang, Mu Li, Hailong Sun.Empirical Methods in Natural Language Processing (EMNLP), 2026.
-
DepUpgrade: Automating Dependency Upgrade through State-Path Exploration
Xiangxi Ma, Yifan An, Wentong Tian, Xuanqi Wang, Qingao Dong, Xiang Gao, Hailong Sun.International Conference on Automated Software Engineering (ASE), 2026.
-
Type-aware LLM-based Test Generation for Python Programs
Runlin Liu, Zhe Zhang, Yunge Hu, Yuhang Lin, Xiang Gao, Hailong Sun.ACM Transactions on Software Engineering and Methodology (TOSEM), 2026.
-
Fusing LLMs and Genetic Algorithm for High-Quality Unit Test Generation
Yiwen Fu, Xiang Gao, Binhang Qi, Yuan Yuan, Hailong Sun.ACM Transactions on Software Engineering and Methodology (TOSEM), 2026.
-
Vulnerability Identification by Harnessing Inter-connected Multi-Source Information
Liyou Chen, Hailong Suna, Xiang Gao, Lin Shi, Yixin Yang, Yi Xu.Journal of Systems and Software (JSS), 2026.
-
PGS: Effective LLM Code Refinement via Property-Oriented and Structurally Minimal Feedback
Lehan He, Zeren Chen, Zhe Zhang, Xiang Gao, Lu Sheng.International Conference on Machine Learning (ICML), 2026.
Show all 38 papers
-
Efficient Bug Detection by Inferring Implicit API Contract of Pointer State Transition
Xingjing Deng, Yunlong Ma, Xiang Gao, Hailong Sun.International Conference on Dependable Systems and Networks (DSN), 2026.
-
Beyond Superficial Tests: Adversarial Refinement for Reliable Property-Based Testing
Xiao Li, Runlin Liu, Zhe Zhang, Xiang Gao, Hailong Sun.Annual Meeting of the Association for Computational Linguistics (ACL Findings), 2026.
-
Code2Bench: Scaling Source and Rigor for Dynamic Benchmark Construction
Zhe Zhang, Runlin Liu, Aishan Liu, Xingyu Liu, Xiang Gao, Hailong Sun.International Conference on Learning Representations (ICLR), 2026.
-
HapCheck: DSL-Based Static Bug Detection Framework for OpenHarmony
Xitong Zhong, Chang Liu, Runlin Liu, Zifu Xu, Zhengyao Liu, Juqi Zhou, Gang Fan, Mingyi Zhou, Xiang Gao, Li Li.International Conference on Software Engineering, SEIP Track (ICSE), 2026.
-
ModularEvo: Evolving Multi-Task Models via Neural Network Modularization and Composition
Wenrui Long, Binhang Qi, Hailong Sun, ZongZhen Yang, Ruobing Zhao, Xiang Gao.International Conference on Software Engineering (ICSE), 2026.
-
Understanding Complex Open-Source Industrial Software Supply Chains
Yijun Shen, Hailong Sun, Guitang Liu, Yao Huang, Xiang Gao.International Conference on Software Quality, Reliability and Security (QRS), 2026.
-
Detecting Vulnerability-Inducing Commits via Multi-Stage Reasoning with LLM-Based Agents
Liyou Chen, Hailong Sun, Xiang Gao, Yue Pan.International Conference on Software Quality, Reliability and Security (QRS), 2026.
-
Scalable Large-Scale Multi-Granularity Code Clone Detection via Clustering Search and Pre-trained Models
Yifan An, Yunlong Ma, Xiang Gao, Hailong Sun.IEEE TRANSACTION ON SOFTWARE ENGINEERING (TSE), 2025.
-
Context-Enhanced Vulnerability Detection Based on Large Language Models
Yixing Yang, Bowen Xu, Xiang Gao, Hailong Sun.ACM Transactions on Software Engineering and Methodology (TOSEM), 2025.
-
UICOMPASS: UI Map Guided Mobile Task Automation via Adaptive Action Generation
Yuanzhang Lin, Zhe Zhang, Rui He, Qingao Dong, Mingyi Zhou, Jing Zhang, Xiang Gao, Hailong Sun.Empirical Methods in Natural Language Processing (EMNLP), 2025.
-
Reference-Based Retrieval Augmentation for Unit Test Generation
Zhe Zhang, Xingyu Liu, Yuanzhang Lin, Xiang Gao, Hailong Sun, Yuan Yuan.ACM Transactions on Software Engineering and Methodology (TOSEM), 2025.
-
Code Property Graph Meets Typestate: A Scalable Framework to Behavioral Bug Detection
Xingjing Deng, Zhengyao Liu, Xitong Zhong, Shuo Hong, Yixin Yang, Xiang Gao, Xuhui Yan, Hailong Sun.International Conference on Software Maintenance and Evolution (ICSME), 2025.
-
Enhanced Vulnerability Localization: Harmonizing Task-Enhanced Tuning and General LLM Prompting
Wentong Tian, Yuanzhang Lin, Xiang Gao, Hailong Sun.International Conference on Software Maintenance and Evolution (ICSME), 2025.
-
Enhancing Automated Vulnerability Repair through Dependency Embedding and Pattern Store
Qingao Dong, Yuanzhang Lin, Xiang Gao, Hailong Sun.IEEE International Conference on Software Analysis, Evolution and Reengineering (SANER), 2025.
-
Understanding vulnerabilities in software supply chains
Yijun Shen, Xiang Gao, Hailong Sun, Yu Guo.Empirical Software Engineering (EMSE), 2025.
-
DynaMO: Protecting Mobile DL Models through Coupling Obfuscated DL Operators
Mingyi Zhou, Xiang Gao, Xiao Chen, Chunyang Chen, John Grundy, Li Li.International Conference on Automated Software Engineering (ASE), 2024.
-
LLM-Based Java Concurrent Program to ArkTS Converter
Runlin Liu, Yuhang Lin, Yunge Hu, Zhe Zhang, Xiang Gao.International Conference on Automated Software Engineering Tool (ASE), 2024.
-
API Misuse Detection via Probabilistic Graphical Model
Yunlong Ma, Wentong Tian, Xiang Gao, Hailong Sun, Li Li.International Symposium on Software Testing and Analysis (ISSTA), 2024.
-
ProveNFix: Temporal Property guided Program Repair
Yahui Song, Xiang Gao, Wenhua Li, Wei Ngan Chin, Abhik Roychoudhury.
International Conference on the Foundations of Software Engineering (FSE), 2024.
-
Investigating and Detecting Silent Bugs in PyTorch Programs
Shuo Hong, Hailong Sun, Xiang Gao#, Shin Hwei Tan.
International Conference on Software Analysis, Evolution and Reengineering (SANER), 2024.
-
Reducing False Positives of Static Bug Detectors through Code Representation Learning
Yixin Yang, Ming Wen, Xiang Gao, Yuting Zhang, Hailong Sun.
International Conference on Software Analysis, Evolution and Reengineering (SANER), 2024.
-
Automated Fixing of Web UI Tests via Iterative Element Matching
Yuanzhang Lin, Guoyao Wen, Xiang Gao.
International Conference on Automated Software Engineering (ASE) 2023, 2023.
-
Automated Repair of Programs from Large Language Models
Zhiyu Fan, Xiang Gao#, Martin Mirchev, Abhik Roychoudhury, Shin Hwei Tan.
International Conference on Software Engineering (ICSE) 2023, 2023.
-
Template-based Neural Program Repair
Xiangxin Meng, Xu Wang, Hongyu Zhang, Hailong Sun, Xudong Liu, Chunming Hu.The 45th International Conference on Software Engineering (ICSE), 2023.
-
A Collaboration-Aware Approach to Profiling Developer Expertise with Cross-Community Data
Xiaotao Song, Jiafei Yan, Yuexin Huang, Hailong Sun, Hongyu Zhang.The 22nd IEEE International Conference on Software Quality, Reliability, and Security (QRS), 2022.
-
Patching Weak Convolutional Neural Network Models through Modularization and Composition
Binhang Qi, Hailong Sun, Xiang Gao, Hongyu Zhang.
IEEE/ACM International Conference on Automated Software Engineering (ASE), 2022.
-
Program Vulnerability Repair via Inductive Inference
Yuntong Zhang, Xiang Gao, Gregory J. Duck, Abhik Roychoudhury.
ACM International Symposium on Software Testing and Analysis (ISSTA), 2022.
-
Improving Fault Localization and Program Repair with Deep Semantic Features and Transferred Knowledge
Xiangxin Meng, Xu Wang, Hongyu Zhang, Hailong Sun, Xudong Liu.The 44th International Conference on Software Engineering (ICSE), 2022.
-
APIfix: Output-Oriented Program Synthesis for Combating Breaking Changes in Libraries
Xiang Gao, Arjun Radhakrishna, Gustavo Soares, Ridwan Shariffdeen, Sumit Gulwani, Abhik Roychoudhury.
Object-Oriented Programming, Systems, Languages, and Applications (OOPSLA), 2021.
-
Automated Patch Backporting in Linux (Experience Paper)
Ridwan Shariffdeen, Xiang Gao, Gregory J. Duck, Shin Hwei Tan, Julia Lawall, Abhik Roychoudhury.
International Symposium on Software Testing and Analysis (ISSTA), 2021.
-
Learning to Handle Exceptions
Jian Zhang, Xu Wang, Hongyu Zhang, Hailong Sun, Yanjun Pu, Xudong Liu.The 35th IEEE/ACM International Conference on Automated Software Engineering (ASE), 2020.
-
Retrieval-based Neural Source Code Summarization
Jian Zhang, Xu Wang, Hongyu Zhang, Hailong Sun, Xudong Liu.The 42nd International Conference on Software Engineering (ICSE), 2020.
IEEE TCSE Distinguished Paper Award
IEEE TCSE Distinguished Paper Award
Distinguished Artifact Award
Our Team
Faculty
 sunhl [at] buaa.edu.cn
Students
Ph.D. Students
Yijun Shen
Ph.D.
Software Supply Chain
Liyou Chen
Ph.D.
Vulnerability recognition
Qingao Dong
Ph.D.
Vulnerability Repair
Wentong Tian
Ph.D.
LLM for vulnerability analysis
Yunlong Ma
Ph.D.
Combining static analysis with LLM
Yixin Yang
Ph.D.
Vulnerability detection
Yuanzhang Lin
Ph.D.
UI Testing
Chenfan Li
Ph.D.
Test generation
Yiwen Fu
Ph.D.
Test generation
Ming Li
Ph.D.
Software Supply Chain

Yao Huang
Ph.D.
UI test
Runlin Liu
Ph.D.
Agentic System Engineering
Zifu Xu
Ph.D.
Agentic System Engineering
Master's Students
Chang Liu
Master
static analysis
Rui He
Master
UI automation
Xingjing Deng
Master
Static analysis
Xingyu Liu
Master
fuzzing
Yifan An
Master
clone detection
Ruiyang Xu
Master
Software Supply Chain
Xiao Li
Master
Test generation
Xitong Zhong
Master
Static analysis
Juqi Zhou
Master
UI Agent
Xiaohan Cao
Master
TBD
Former Students
Former Students
Bowen Xu
Master 2023
Move to *** Lab
Hao Gao
Master 2023
Move to JD.com
Yi Xu
Master 2023
Move to Huawei
Yu Guo
Master 2023
Move to JD.com
Zhe Zhang
Master 2023
Move to ByteDance
Zuozhou Zhang
Master 2023
Move to Meituan
Shuo Hong
Master 2022
Move to MiHoYo
Chunyi Xu
Master 2021
Moved to Agricultural Bank of China
Rui Sui
Master 2021
Moved to Agricultural Bank of China
Chongpeng Li
Master 2020
Haoqian He
Master 2020
Yongqiang Yang
Master 2020